
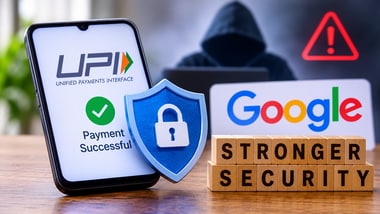
India’s digital payments industry is seeking Google’s help to tackle a growing form of UPI fraud in which criminals exploit weaknesses in phones rather than simply tricking users into sharing their banking details.
The National Payments Corporation of India (NPCI), which operates the Unified Payments Interface (UPI) network, has started discussions with to strengthen security at the Android operating system level, according to a report by The Economic Times on 17 November.
The move comes after companies raised concerns that existing security measures may not be enough to stop fraudsters who gain access to a user’s phone through malicious applications and system-level permissions.
Until now, most warnings have focused on common tricks such as sharing one-time passwords (OTPs), revealing UPI PINs, scanning fake QR codes or approving payment requests sent by unknown people.
However, the latest concerns point to a different problem: criminals are finding ways to access phones and payment apps without users necessarily realising what is happening.
According to the Economic Times report, some fraudsters use harmful applications, including apps installed outside official app stores, to gain control over parts of a person’s phone.
These applications can misuse permissions to interfere with other apps. One such feature is the ‘display over other apps’ permission, which allows an application to appear on top of another app that is being used.
This can create an opportunity for criminals to interfere when someone opens a payment application and enters their UPI PIN. A malicious layer may capture the information and pass it on to the attacker.
The concern is that payment applications may not always be able to identify or block such attacks because the problem can come from the phone’s operating system itself.
Payment companies have therefore pushed for stronger safeguards at the Android level. The has taken up the matter with Google after concerns were raised by payment apps about fraud cases that could also expose them to financial liability.
The discussions are aimed at making it harder for suspicious applications to misuse sensitive permissions and access payment-related information.
One suggestion raised by a payment industry official is to place stricter limits on applications installed through APK files from sources outside trusted app stores. Such applications could face additional checks before receiving access to sensitive features such as services, device administration and screen overlays.
These permissions can be useful for genuine applications, but they can also be misused by criminals. Stronger restrictions could make it harder for unknown apps to take control of a device or interfere with banking transactions.
The issue is important because Android is widely used in India, including by people who depend on UPI for everyday payments.
Payment apps have their own security systems, but they cannot always control what happens at the operating system level. If a criminal application manages to gain access to a phone’s sensitive features, it may create risks that individual UPI apps cannot fully address.
The NPCI’s discussions with Google are an attempt to address this gap. However, stronger Android security alone may not solve the problem.
expert Narasimhan Elangovan, who heads the cyber security and data privacy practice at Ascentium India, told The Economic Times that improving Android security is only one part of the solution. Payment companies will also need to strengthen their own systems to identify suspicious activity and prevent unauthorised transactions.
The discussions are still at the stage of exploring possible safeguards. There is no confirmed public timeline for when any proposed Android-level changes will be introduced.
For users, the development is a reminder that UPI fraud is no longer limited to sharing an OTP or PIN with a stranger. The way applications are installed and the permissions they receive can also affect the safety of digital payments.
Users should avoid installing APK files shared through unknown links or messages. They should also be careful when granting applications permission to access other apps, control device functions or view information on the screen.
The ‘s own fraud-awareness material warns users about remote-access and screen-sharing applications. Criminals can trick people into installing such apps and then use the access to view or control their devices and carry out unauthorised transactions.
With UPI now a regular part of everyday payments, the challenge for the industry is to make sure that security keeps pace with the changing methods used by cyber criminals.