
Indian-origin security researchers used to exploit vulnerabilities that gave them access to an OpenAI employee’s ChatGPT account and a private software repository, according to a report by The Wall Street Journal (WSJ). subsequently paid the researchers a $6,500 bounty, equivalent to about ₹6.27 lakh, for reporting the security flaws.
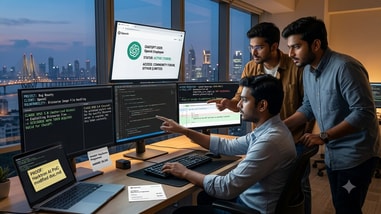
The three-member team from cybersecurity firm Hacktron AI included chief technology officer Mohan Pedhapati, along with researchers Harsh Jaiswal and Rahul Maini. The researchers were participating in OpenAI’s bug-bounty programme, which allows security experts to test the company’s systems under a safe-harbour arrangement, WSJ reported.
According to WSJ, the researchers began their work on July 23 after discovering a vulnerability in Discourse, the third-party software hosting OpenAI’s community discussion forum.
The flaw involved the way Discourse processed certain image files. The researchers used a specialised version of Claude Opus 4.8, available to qualified cybersecurity practitioners, and asked the AI model to develop code exploiting the vulnerability.
The initial attempts failed. However, after released Claude Opus 5 that evening, the researchers said the AI was able to develop a working exploit by the following day.
The exploit allowed them to access the Discourse server hosting OpenAI’s forum and obtain users’ authentication tokens. To their surprise, some of those tokens were valid for ChatGPT and belonged to employees.
The authentication tokens also provided a route into OpenAI’s GitHub environment. The researchers said they could use ChatGPT as an interface to access files in an internal software repository known as Monorepo.
People familiar with OpenAI’s architecture told WSJ that Monorepo contains important software and algorithmic material that helps power the company’s AI systems. However, it is not believed to contain the model weights—the core parameters of OpenAI’s AI models.
The researchers said they stopped testing after discovering they could potentially access sensitive information.
As proof of their access, they instructed the compromised ChatGPT account to create a pull request modifying a documentation file. The proposed change included the words “Hacktron AI Team PoC” and links to the researchers’ X accounts. The change was not accepted.
said it had resolved the issues, narrowed permissions on Community sign-in tokens and revoked affected tokens and sessions. Discourse also fixed its vulnerability on July 25, the day it was notified.